Find Security Flaws Before Attackers Do |
Automated scanners only find basic bugs. Our certified ethical hackers manually exploit application logic, construct custom exploit paths, and help you deploy code patches.
Penetration Testing That Scales With Your Business
Security needs evolve as your business grows. SysopHost delivers targeted penetration testing aligned with your business size, technology, risk profile, and security priorities.
Startups & Small Businesses
Build securely from day one.
Protect your applications — Identify vulnerabilities in websites, APIs, and cloud environments.
Prioritize critical risks — Focus on vulnerabilities that matter most to your business.
Mid-Sized Businesses
Stay secure as your attack surface grows.
Discover security gaps — Test your applications, networks, cloud, and external assets.
Support compliance — Get clear reports and actionable remediation guidance.
Enterprises & Global Organizations
Test complex environments with confidence.
Assess your attack surface — Test applications, APIs, networks, cloud, and remote access.
Strengthen enterprise security — Identify realistic attack paths and align findings with your security framework.
Trusted By Businesses. Driven By Experts. Validated By Testing.
How penetration testing is performed depends on the level of access and visibility provided during the engagement. External, internal, and hybrid attack paths require different testing perspectives. At SysopHost, our flexible testing models adapt to your environment, objectives, and security requirements.

Black Box Testing
Black box penetration testing simulates how an external attacker would view and target your systems without insider access. It helps uncover publicly exposed vulnerabilities and exploitable weaknesses before they become security incidents.

White Box Testing
White box penetration testing provides our experts with detailed access to your environment, including source code, architecture, configurations, and credentials. This deeper visibility helps uncover code-level flaws and system weaknesses that automated tools may overlook.

Gray Box Testing
Gray box penetration testing simulates threats from users with limited access to your systems. By replicating compromised accounts or internal users, we identify privilege escalation opportunities, access-control weaknesses, and potential lateral movement risks.
You Can’t Protect What You Don’t Test
The Trusted Tech Stack Behind SysopHost Penetration Testing
As a trusted penetration testing provider, SysopHost uses proven security tools to uncover vulnerabilities across applications, networks, APIs, cloud environments, mobile devices, and wireless infrastructure.
Web & Application Security Testing
SysopHost combines automated scanning with expert-led testing to identify vulnerabilities across websites, web applications, servers, and APIs.
Burp Suite
Web and API security testing
OWASP ZAP
Automated vulnerability discovery
Nikto
Web server security assessment
Acunetix
Automated web vulnerability scanning
Dirbuster
Hidden directory and file discovery
Wapiti
Black-box web application testing
What Makes Our Penetration Testing Worth It
Most security assessments end with a report. At SysopHost, our penetration testing starts with a clear strategy and ends with actionable results. Why? We don’t simply list vulnerabilities. We help you understand attack paths and prioritize what to fix first based on business impact.
Prioritize vulnerabilities
linked to compliance gaps and operational disruption.
Perform manual assessments
to uncover logic flaws and privilege risks automated tools may miss.
Deliver technical reports
with step-by-step remediation guidance for every identified vulnerability.
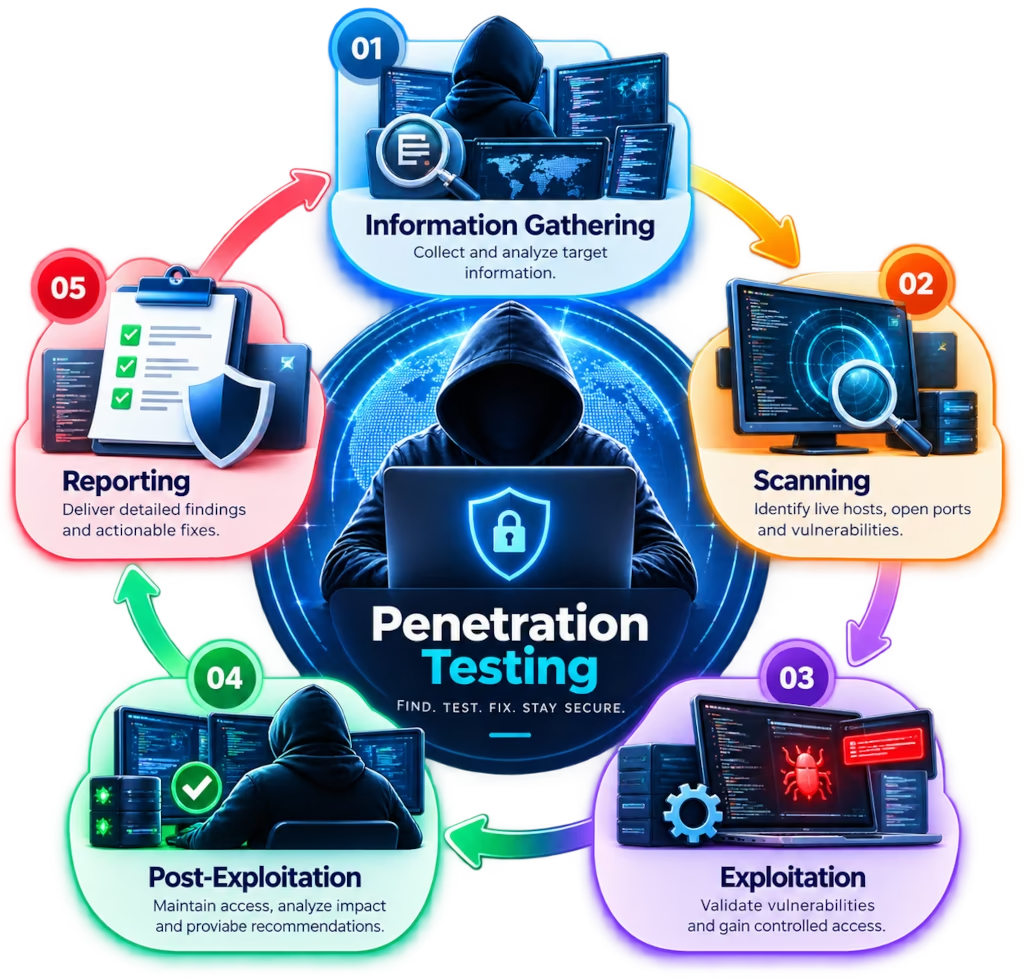
Why Clients Trust Our Proven Penetration Testing Process
We don’t follow a checklist. We follow real-world threats. Our penetration testing process mirrors attacker behavior, from reconnaissance and vulnerability discovery to exploitation and escalation. You get more than testing—a clear understanding of what’s exposed, its impact, and what to fix first.
Define Scope & Goals
Your business objectives, environments, applications, and compliance requirements shape the testing scope from the beginning.
Set Engagement Rules
Before testing begins, our team establishes clear boundaries and rules to protect your production systems and teams.
Run Reconnaissance
We perform reconnaissance to uncover external exposure, internal clues, and potential attack paths that could lead to compromise.
Identify Vulnerabilities
Using automated tools and manual techniques, we identify weaknesses across authentication, configurations, applications, APIs, and logic.
Exploitation & Attack Simulation
Our security experts safely simulate real-world attacks to determine how far an attacker could penetrate your environment.
Post-Exploitation Analysis
After gaining access, we analyze potential next steps to understand how attackers could expand privileges or reach sensitive systems.
Report Exploitation Results
Our reports go beyond technical findings, prioritizing vulnerabilities based on severity, business impact, exposure, and operational risk.
Fix Issues & Retest
After remediation, we perform follow-up testing to validate fixes and confirm that critical vulnerabilities have been properly resolved.
Penetration Testing FAQ
Clear answers on system safety during mock hacking.